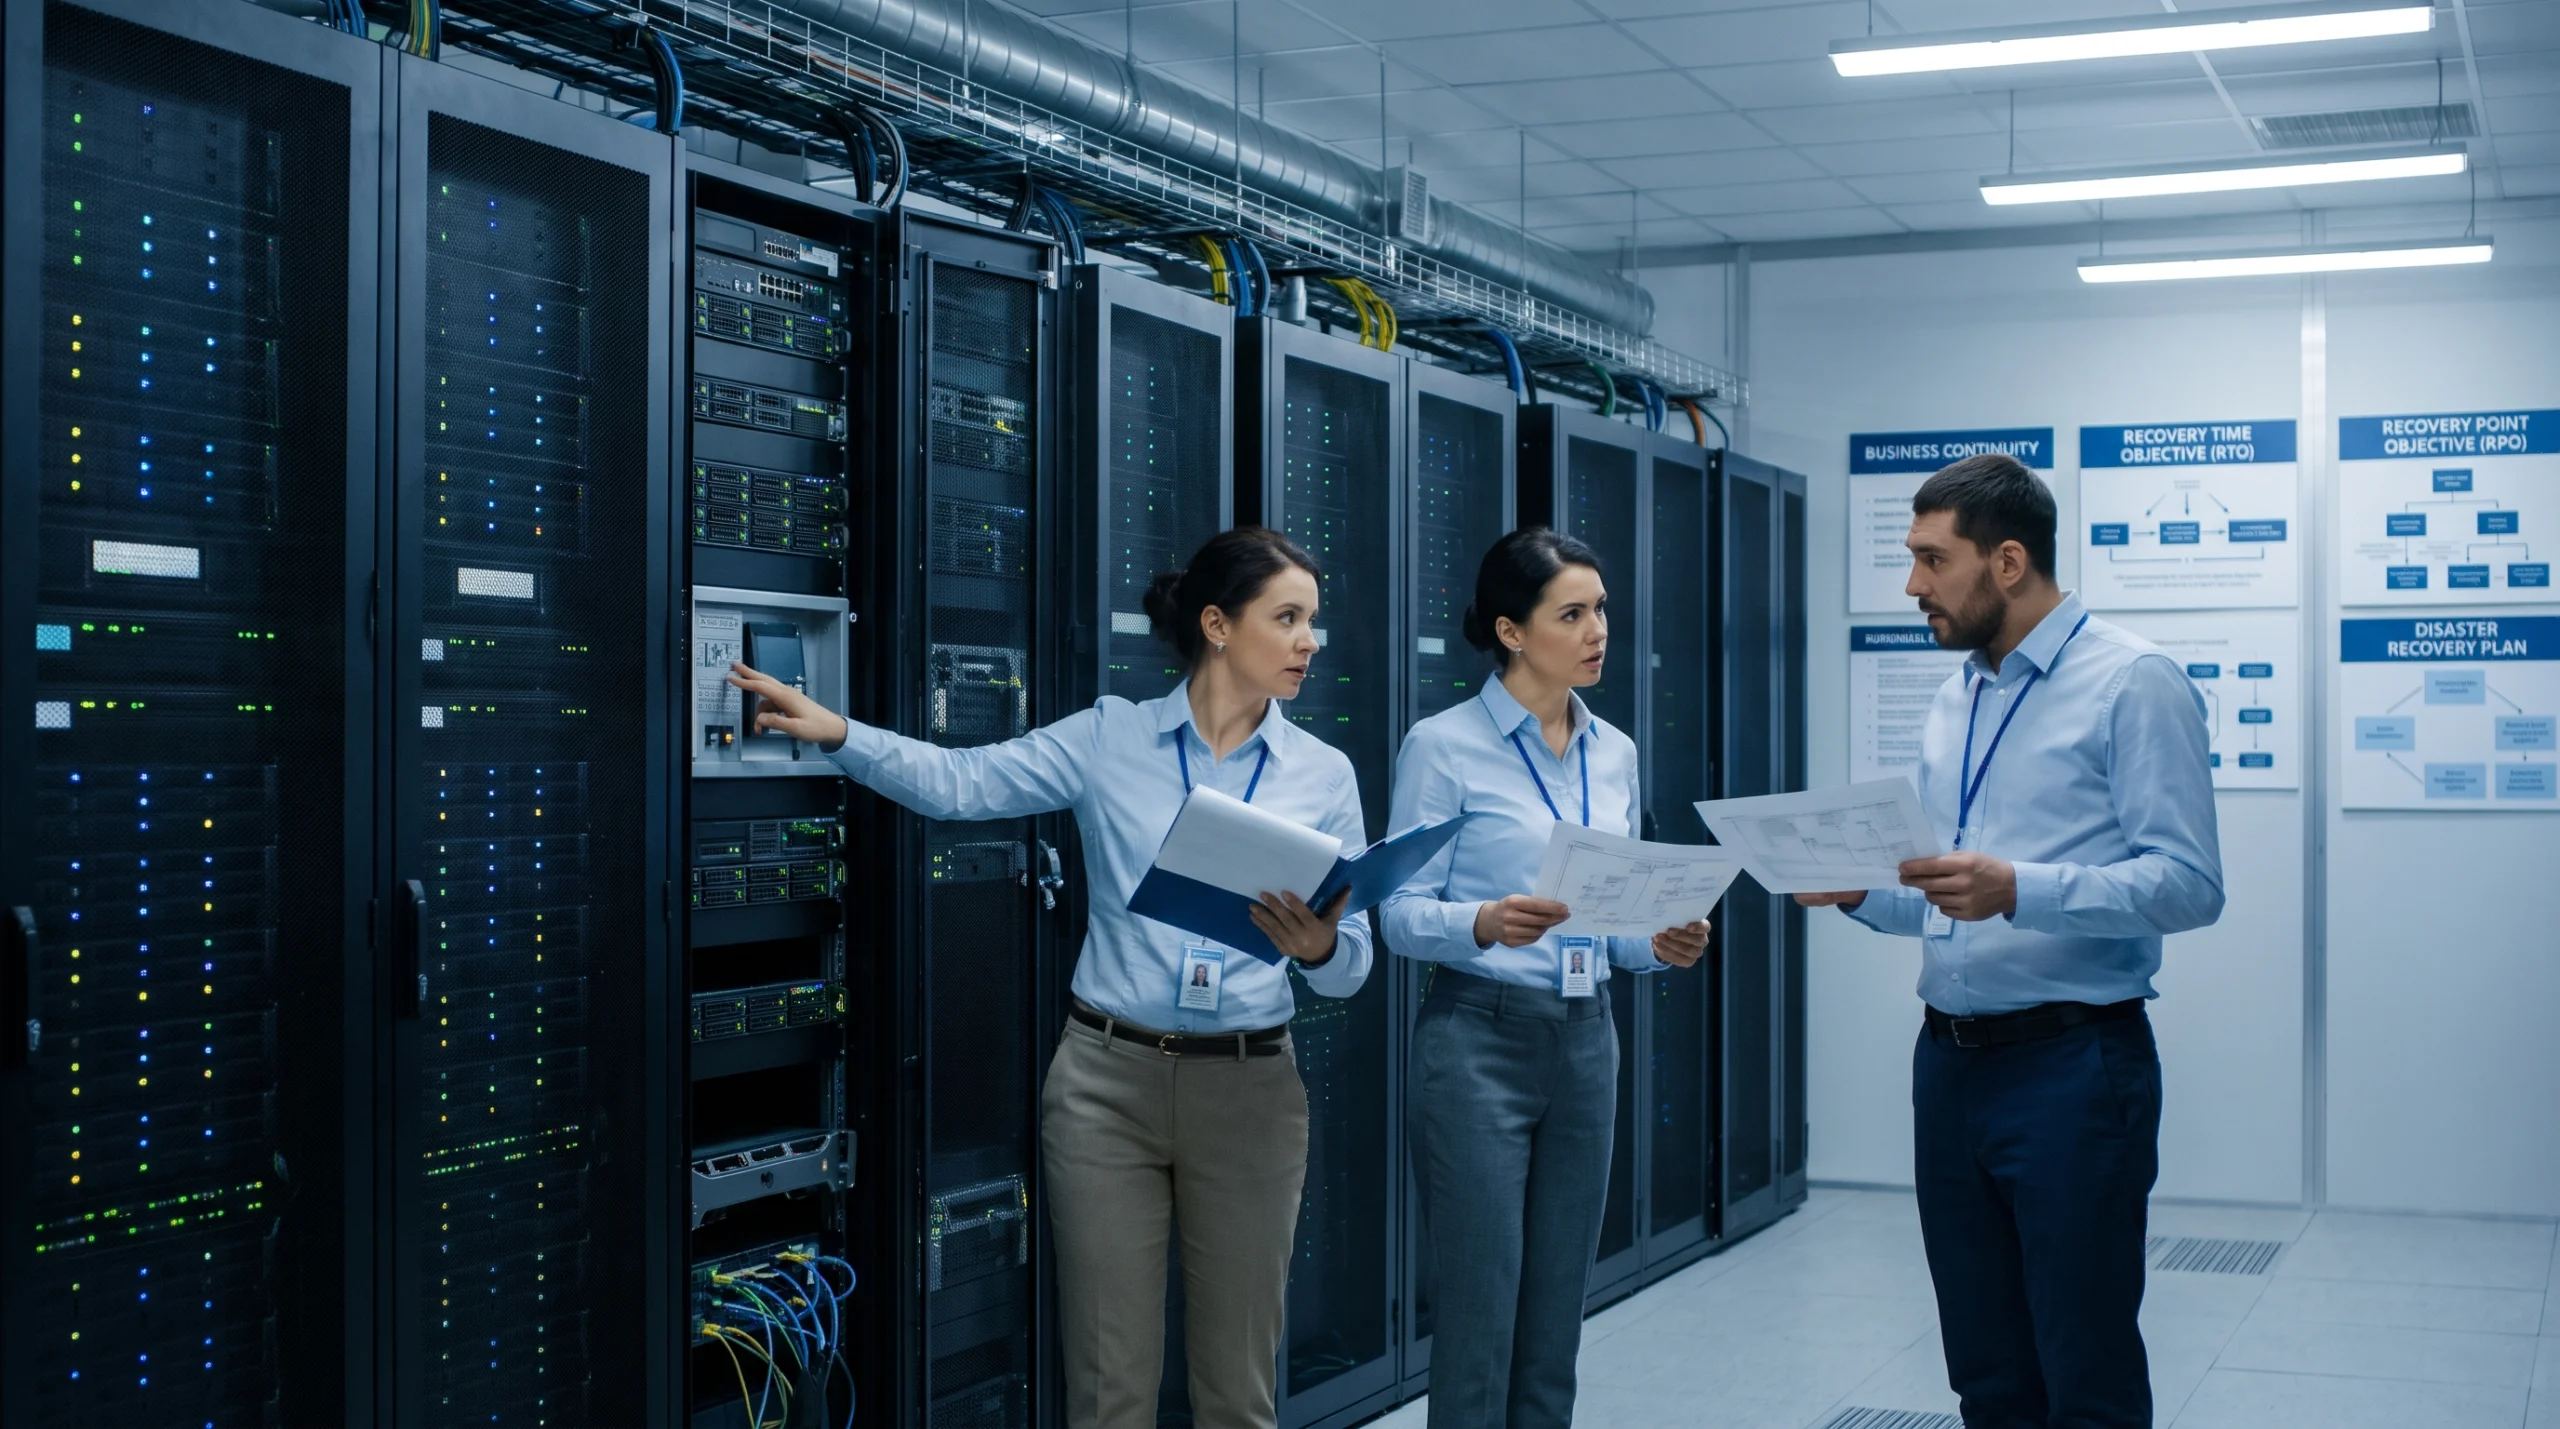
In enterprise corporate computing, systems engineers rely on rigorous business continuity standards to ensure digital infrastructure can survive devastating catastrophic failures. Two fundamental benchmarks govern this discipline: the recovery time objective, which defines how many hours a system can remain offline, and the recovery point objective, which defines how much recent data loss an organization can tolerate. While corporate information technology departments spend millions testing disaster recovery drills, everyday technology users rarely apply these proven principles to their personal electronic devices until an unexpected disaster strikes.
The Cold Start Trap in Modern Cloud Authentication
Most smartphone users maintain a false sense of security believing that automated cloud synchronization protects them completely against hardware loss or theft. Consider a realistic emergency scenario where an individual loses both their laptop and smartphone on a Friday evening while traveling. After purchasing a replacement smartphone, the individual attempts to sign into their primary cloud backup account to restore their personal data. However, the cloud security gateway demands two factor authentication by sending an authorization prompt to the stolen device. Because the user lacks an independent authentication method, what should have been a two hour hardware replacement transforms into a two week account recovery lockout. Maintaining offline physical security keys prevents the sudden digital paralysis created by modern authentication loops.
Categorizing Personal Assets by Data Loss Tolerance
A resilient personal continuity plan requires recognizing that distinct categories of personal data possess vastly different tolerances for permanent loss. A recovery point objective measures the maximum acceptable period of data loss that an individual can endure before critical damage occurs. For critical security credentials, such as password manager databases, financial account passkeys, and encryption master keys, the data loss tolerance is absolute zero. In contrast, family photo libraries and downloaded multimedia files can easily tolerate a thirty day backup lag without compromising personal security. Understanding these data tiers ensures that individuals allocate backup resources toward irreplaceable credentials rather than wasting effort on easily replaceable files.
The Cellular Electronic SIM Provisioning Bottleneck
The universal adoption of embedded electronic subscriber identity modules has revolutionized mobile connectivity while introducing a hidden disaster recovery vulnerability. With physical plastic cards, restoring mobile service was as simple as ejecting the card and inserting it into a backup handset. With modern electronic profiles, installing a mobile carrier service onto a replacement smartphone requires logging into the cellular provider mobile application. However, logging into the cellular provider portal typically requires receiving a one time verification code via text message. This circular verification trap prevents users from restoring their primary telephone number precisely when they need it most. Keeping printed carrier account recovery codes in a secure physical location is vital to bypass circular authentication barriers.
Assembling a Practical Two Hour Personal Emergency Kit
Individuals can dramatically compress their personal restoration timeline by constructing a dedicated emergency recovery kit stored in a secure fireproof location. A comprehensive kit should contain two physical hardware authentication keys, a printed emergency sheet documenting master account recovery phrases, and a pre configured secondary smartphone. Updating the three two one backup rule to include hardware encryption keys and offline authentication credentials ensures that users can rebuild their digital identity within two hours. Storing an independent encrypted copy of critical digital vaults in an offsite location protects household records from physical residential disasters.
Navigating Passwordless Logins and Local Artificial Intelligence Memory
The widespread industry transition toward biometric logins and device bound passkeys offers superior defense against online phishing scams while creating new personal restoration challenges. Device bound cryptographic credentials cannot be easily exported to third party storage, demanding disciplined enrollment of secondary backup hardware. Furthermore, as users deploy personal artificial intelligence assistants that maintain local vector memory databases, losing an unbacked local machine permanently erases months of customized organizational context. Establishing disciplined personal disaster recovery protocols guarantees that your digital life remains completely resilient against unexpected hardware failures.